Map the official objectives.
Read the current AWS objectives and make a short list of the areas you need to revisit before booking SCS-C03.
AWS CERTIFICATION STUDY GUIDE
Validates advanced skills in securing AWS workloads and understanding security controls.
Download Revizo
Validates advanced skills in securing AWS workloads and understanding security controls.
Exam details are based on the available AWS catalogue information. Confirm current requirements with the exam provider before booking.
Use the provider's current objectives as your source of truth, then organise your Revizo sessions around AWS services, cloud concepts and the decisions expected in the certification. The SCS-C03 exam is listed as Multiple choice and multiple response questions; your starting point should reflect 2+ years of AWS security experience.
Read the current AWS objectives and make a short list of the areas you need to revisit before booking SCS-C03.
Select SCS-C03 in Revizo and use focused question sessions to test one topic or decision type at a time, rather than relying on a single long cram session.
Use your results to return to incorrect answers, revisit the official material behind them and repeat short SCS-C03 practice sessions until the gaps are clearer.
FREE PRACTICE PREVIEW
Review each question, its correct answer and any available source explanation before continuing your certification study in Revizo.
Answers & available explanations
QUESTION 1
A security engineer is troubleshooting an AWS Lambda function that is named MyLambdaFunction. The function is encountering an error when the function attempts to read the objects in an Amazon S3 bucket that is named DOC-EXAMPLE-BUCKET. The S3 bucket has the following bucket policy: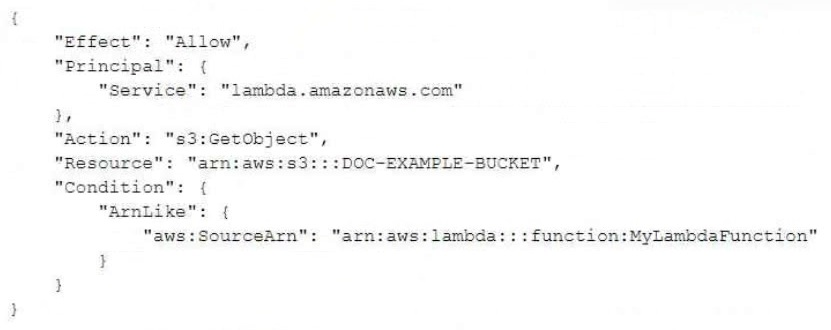
Which change should the security engineer make to the policy to ensure that the Lambda function can read the bucket objects?
Correct answer: C
QUESTION 2
HOTSPOT -
A company is building a web application that needs to authenticate external users across multiple microservices that the company hosts on Amazon Elastic Container Service (Amazon ECS). The solution must use temporary credentials and minimize the management overhead required to maintain user databases.
Select and order the correct steps from the following list to implement a secure authentication strategy that meets these requirements. Select each step one time or not at all.
Configure Amazon Cognito user pools for user authentication.
Set up an IAM role for each microservice. Grant each role appropriate permissions.
Implement an Amazon API Gateway HTTP API with AWS Lambda authorizers to validate tokens before forwarding requests to microservices.
Create an Amazon DynamoDB table to store user credentials for each microservice.
Create an Amazon Cognito application client to interact with the web application.
Set up AWS IAM Identity Center to give users access to the microservices.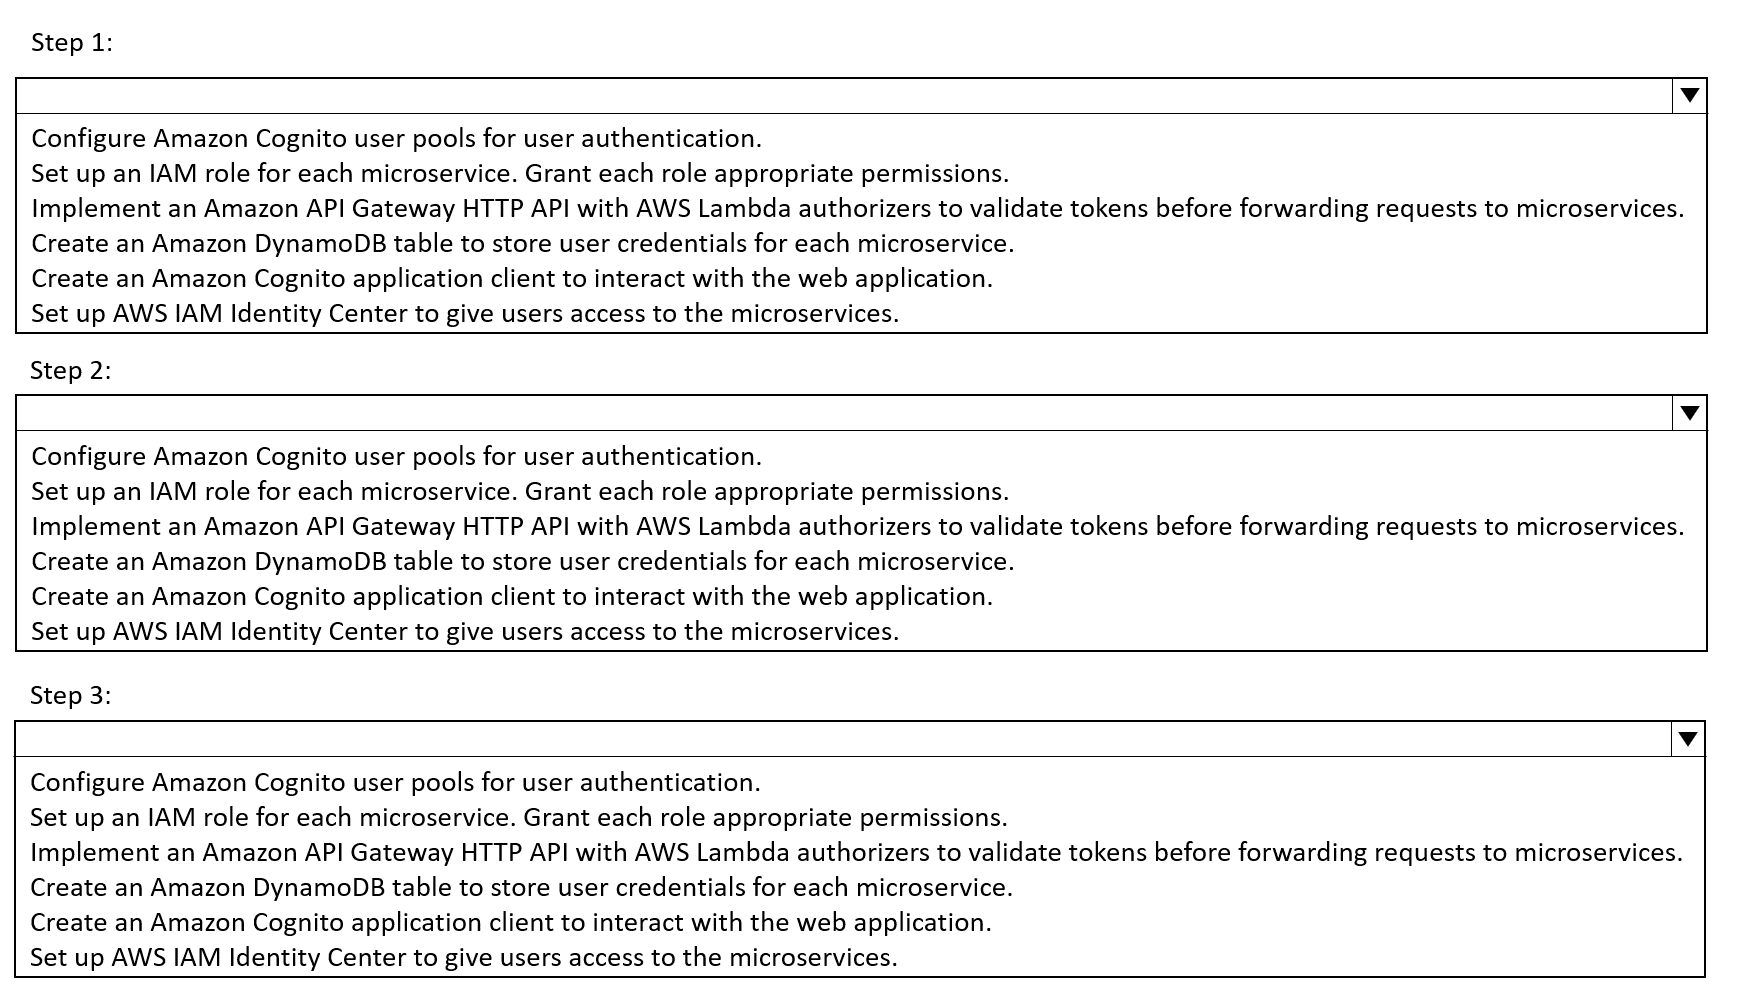
Correct answer: Item 1: A · Item 2: E · Item 3: C
QUESTION 3
An AWS account administrator created an IAM group and applied the following managed policy to require that each individual user authenticate using multi-factor authentication: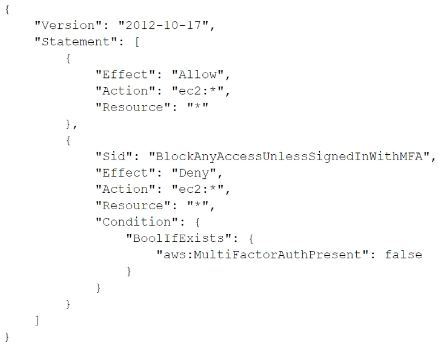
After implementing the policy, the administrator receives reports that users are unable to perform Amazon EC2 commands using the AWS CLI.
What should the administrator do to resolve this problem while still enforcing multi-factor authentication?
Correct answer: B
QUESTION 4
A company is using AWS Organizations with the default SCP. The company needs to restrict AWS usage for all AWS accounts that are in a specific OU.
Except for some desired global services, the AWS usage must occur only in the eu-west-1 Region for all accounts in the OU. A security engineer must create an SCP that applies the restriction to existing accounts and any new accounts in the OU.
Which SCP will meet these requirements?
Correct answer: C
QUESTION 5
HOTSPOT -
A security engineer needs to implement AWS IAM Identity Center with an exlemai identity provider (IdP).
Select and order the correct steps from the following list to meet this requirement. Select each step one time or not at all.
Configure the external IdP as the identity source in IAM Identity Center.
Create an IAM role that has a trust policy that specifics the IdP's API endpoint.
Enable automatic provisioning in IAM Identity Center settings
Enable automatic provisioning in the external IdP.
Obtain the SAML metadata from IAM Identity Center.
Obtain the SAML metadata from the external IdP.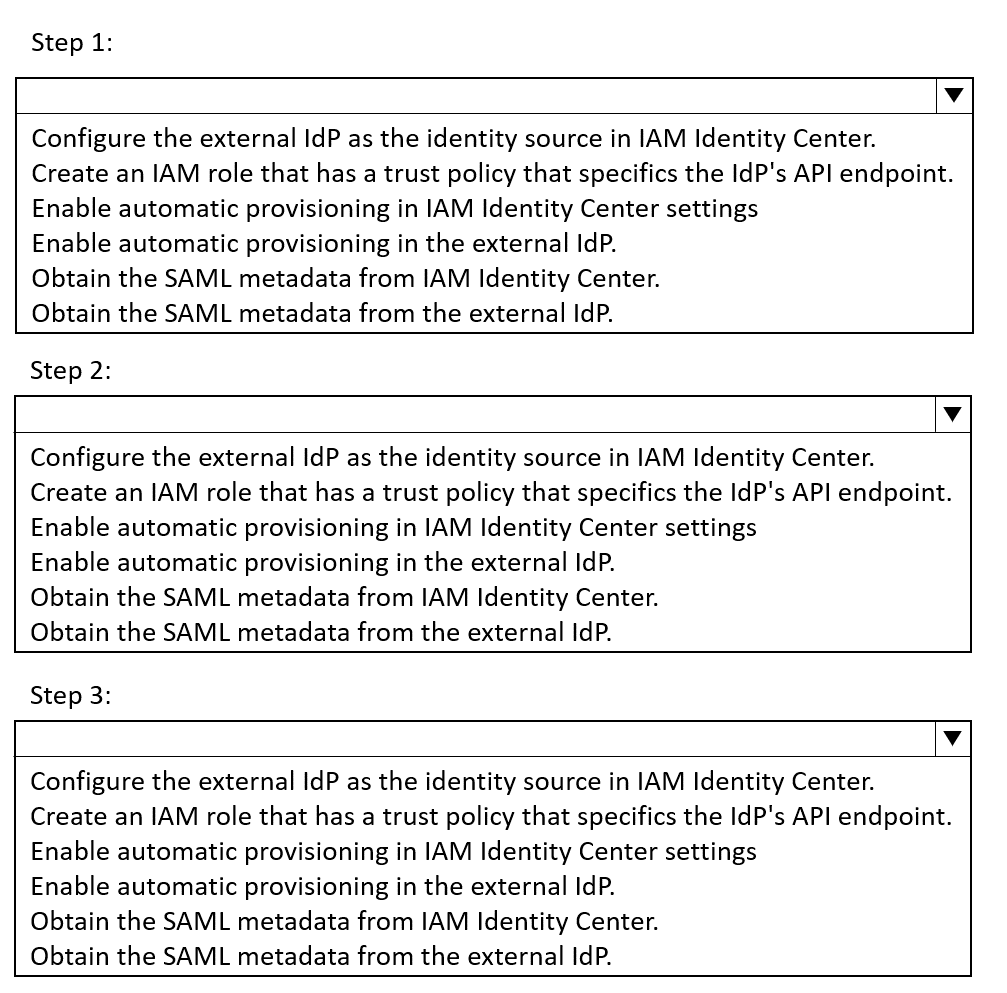
Correct answer: Item 1: F · Item 2: A · Item 3: C
QUESTION 6
What is the effect of the following AWS Key Management Service (AWS KMS} key policy that is attached to a customer managed key?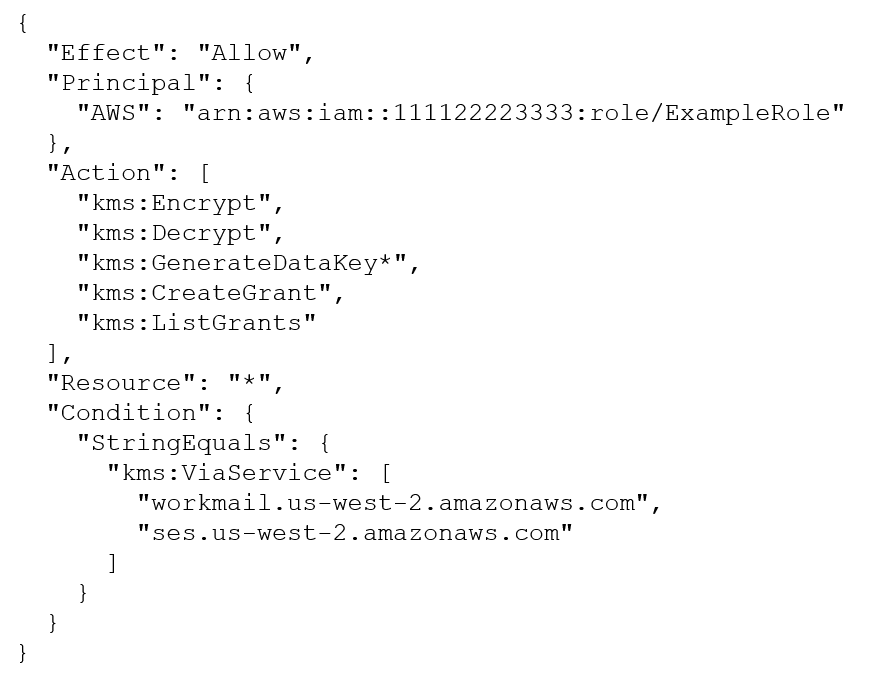
Correct answer: C
QUESTION 7
A company wants to deny a specific federated user named Bob access to an Amazon S3 bucket named DOC-EXAMPLE-BUCKET. The company wants to meet this requirement by using a bucket policy. The company also needs to ensure that this bucket policy affects Bob's S3 permissions only. Any other permissions that Bob has must remain intact.
Which policy should the company use to meet these requirements?
Correct answer: B
QUESTION 8
HOTSPOT -
A company is designing its security monitoring strategy for an existing sensitive workload on AWS. The security team has identified several scenarios that require monitoring strategies.
Select the correct monitoring strategy from the following list for each monitoring scenario. Select each monitoring strategy one time.
Automatically isolate Amazon EC2 distances when malware detection findings are confirmed.
Correlate security findings from multiple AWS detection services to identify multi-stage attacks.
Detect when privileged users perform an unusually high volume of resource deletion operations.
Identify patterns of more than 50 failed authentication attempts from specific IP addresses in 1 hour.
Monitor network traffic patterns especially large data transfers to external IP addresses outside normal office hours.
Configure VPC Flow Logs with Amazon CloudWatch Logs Insights queries to analyze traffic volume and destination patterns during specific time windows.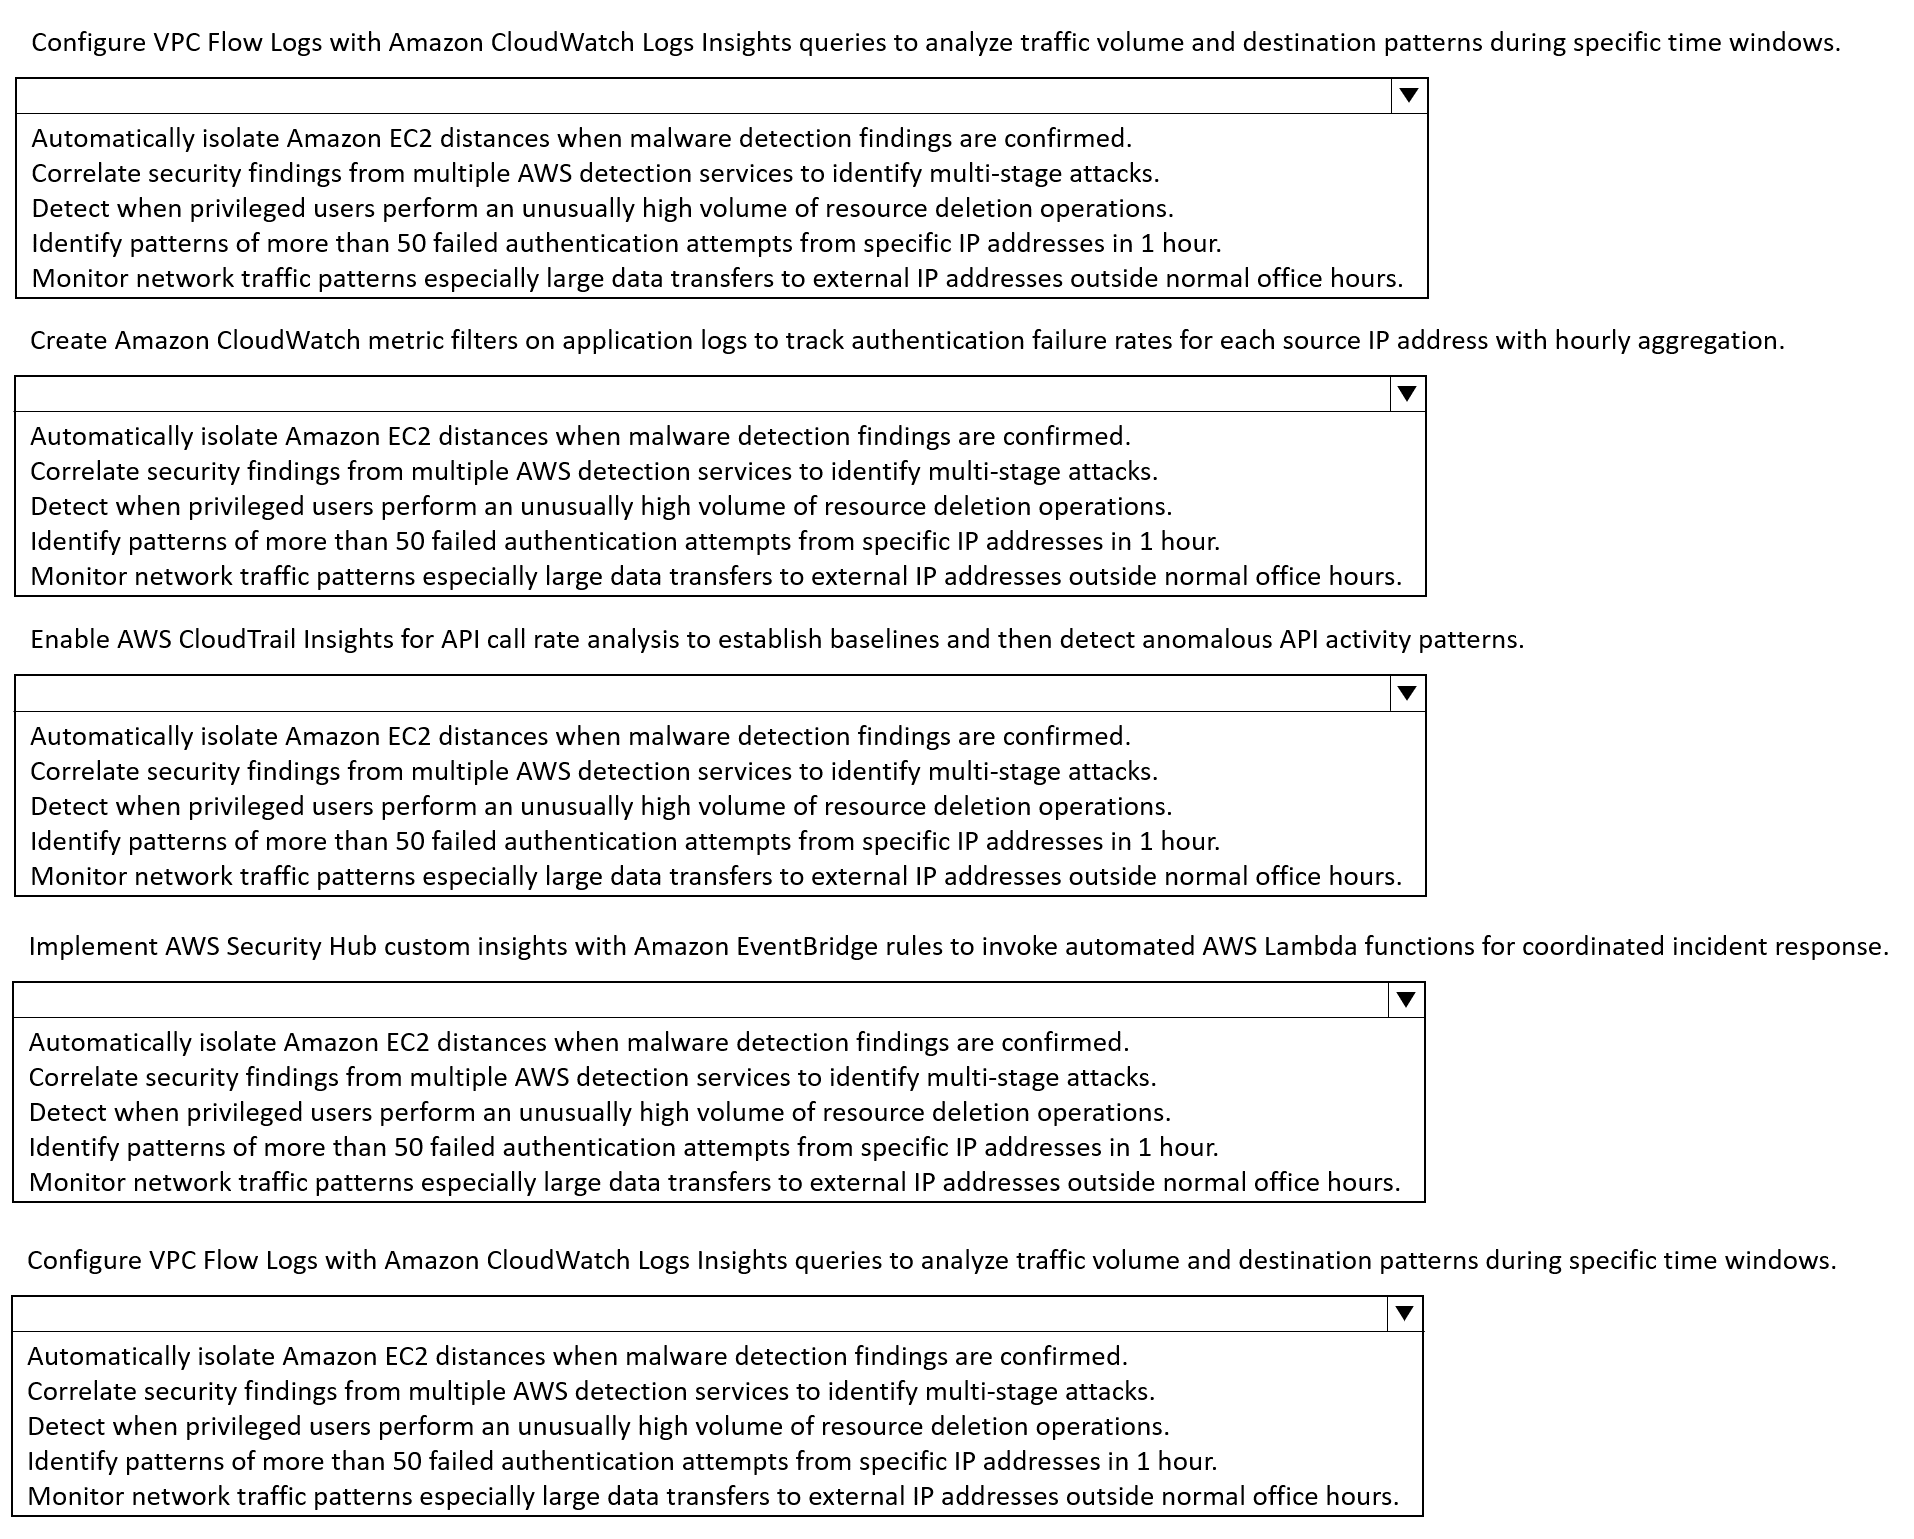
Correct answer: Item 1: E · Item 2: D · Item 3: C · Item 4: A · Item 5: B
QUESTION 9
A company needs a solution to protect critical data from being permanently deleted. The data is stored in Amazon S3 buckets.
The company needs to replicate the S3 objects from the company's primary AWS Region to a secondary Region to meet disaster recovery requirements. The company must also ensure that users who have administrator access cannot permanently delete the data in the secondary Region.
Which solution will meet these requirements?
Correct answer: A
QUESTION 10
A security engineer is responding to an incident that is affecting an AWS account. The ID of the account is 1234156789012. The attack created workloads that are distributed across multiple AWS Regions.
The security engineer contains the attack. The security engineer removes all compute and storage resources from all affected Regions. However, the attacker also created an AWS KMS key. The key policy on the KMS key explicitly allows IAM principal kms:* permissions.
The key was scheduled to be deleted the previous day. However, the key is still enabled and usable. The key has an ARN of arn:aws;kms:us-east-2:123456789012:key/mrk-0bb0212cd9864fdea0dcamzo26efb5670. The security engineer must delete the key as quickly as possible.
Which solution will meet this requirement?
Correct answer: B
QUESTION 11
A company has installed a third-party application that is distributed on several Amazon EC2 instances and on-premises servers. Occasionally, the company's IT team needs to use SSH to connect to each machine to perform software maintenance tasks. Outside these time slots, the machines must be completely isolated from the rest of the network. The company does not want to maintain any SSH keys. Additionally, the company wants to pay only for machine hours when there is an SSH connection.
Which solution will meet these requirements?
Correct answer: B
QUESTION 12
A company runs several applications on Amazon Elastic Kubernetes Service (Amazon EKS). The company needs a solution to detect any Kubernetes security risks by monitoring Amazon EKS audit logs in addition to operating system, networking, and file events. The solution must send email alerts for any identified risks to a mailing list that is associated with a security team.
Which solution will meet these requirements?
Correct answer: C
QUESTION 13
A company allows users to download its mobile app onto their phones. The app is MQTT based and connects to AWS IoT Core lo subscribe la specific client-related topics.
Recently, the company discovered that some malicious attackers have been trying to get a Trojan horse onto legitimate mobile phones. The Trojan horse poses as the authentic application and uses a client ID with injected special characters to gain access to topics outside the client's privilege scope.
Which combination of actions should the company take to prevent this threat? (Choose two.)
Correct answer: A, E
QUESTION 14
A security engineer wants to evaluate configuration changes to a specific AWS resource to ensure that the resource meets compliance standards. However, the security engineer is concerned about a situation in which several configuration changes are made to the resource in quick succession. The security engineer wants to record only the latest configuration of that resource to indicate the cumulative impact of the set of changes.
Which solution will meet this requirement in the MOST operationally efficient way?
Correct answer: B
QUESTION 15
A security engineer needs to implement a solution to create and control the keys that a company uses for cryptographic operations. The security engineer must create symmetric keys in which the key material is generated and used within a custom key store that is backed by an AWS CloudHSM cluster.
The security engineer will use symmetric and asymmetric data key pairs for local use within applications. The security engineer also must audit the use of the keys.
How can the security engineer meet these requirements?
Correct answer: D
QUESTION 16
A company is running an application on Amazon EC2 instances in an Auto Scaling group. The application stores logs locally. A security engineer noticed that logs were lost after a scale-in event. The security engineer needs to recommend a solution to ensure the durability and availability of log data. All logs must be kept for a minimum of 1 year for auditing purposes.
What should the security engineer recommend?
Correct answer: C
QUESTION 17
A company is using AWS to run a long-running analysis process on data that is stored in Amazon S3 buckets. The process runs on a fleet of Amazon EC2 instances that are in an Auto Scaling group. The EC2 instances are deployed in a private subnet of a VPC that does not have internet access. The EC2 instances and the S3 buckets are in the same AWS account.
The EC2 instances access the S3 buckets through an S3 gateway endpoint that has the default access policy. Each EC2 instance is associated with an instance profile role that has a policy that explicitly allows the s3:GetObject action and the s3:PutObject action for only the required S3 buckets.
The company learns that one or more of the EC2 instances are compromised and are exfiltrating data to an S3 bucket that is outside the company's organization in AWS Organizations. A security engineer must implement a solution to stop this exfiltration of data and to keep the EC2 processing job functional.
Which solution will meet these requirements?
Correct answer: B
QUESTION 18
A company recently experienced a malicious attack on its cloud-based environment. The company successfully contained and eradicated the attack A security engineer is performing incident response work. The security engineer needs to recover an Amazon RDS database cluster to the last known good version. The database cluster is configured to generate automated backups with a retention period of 14 days. The initial attack occurred 5 days ago at exactly 3:15 PM
Which solution will meet this requirement?
Correct answer: A
QUESTION 19
A security engineer for a company needs to design an incident response plan that addresses compromised IAM user account credentials. The company uses an organization in AWS Organizations and AWS IAM Identify Center to manage user access. The company uses a delegated administrator account to implement AWS Security Hub. The delegated administrator account contains an organizational trail in AWS CloudTrail that logs all events to an Amazon S3 bucket. The company has also configured an organizational event data store that captures all events from the trail.
The incident response plan must provide steps that the security engineer can take to immediately disable any compromised IAM user when the security engineer receives a notification of a security incident.
The plan must prevent the IAM user from being used in any AWS account. The plan must also collect all AWS actions that the compromised IAM user performed across all accounts in the previous 7 days.
Which solution will meet these requirements?
Correct answer: D
QUESTION 20
A security engineer is designing security controls for a fleet of Amazon EC2 instances that run sensitive workloads in a VPC. The security engineer needs to implement a solution to detect and mitigate software vulnerabilities on the EC2 instances.
Which solution will meet this requirement?
Correct answer: A
Choose SCS-C03 in Revizo and work through original, question-by-question practice on your iPhone. Review results, revisit what needs attention and keep your next session tied to one specific certification objective.
Practise SCS-C03 with RevizoNo. Revizo is an independent iPhone app for certification practice. Refer to the provider's official resources for current exam policies and registration.
Use the exam code to select the matching certification in Revizo, then build short, focused sessions around the areas you want to review.
No. Revizo provides original practice questions for certification study. Use the provider's official objectives, documentation and policies as the source of truth for your preparation.
Use the current AWS objectives, documentation and registration guidance as your source of truth. Revizo is designed to support focused practice, not replace the provider's official materials.
Check the official AWS exam page for the latest objectives, registration details and policies.